“Sovereign” is a claim to test before a bank deploys
“Sovereign AI” can sound like a product property: choose a private cloud or on-premises runtime and the question is settled. It is not. A bank still needs to identify the information that enters the workload, every place prompts and outputs can travel, who can operate the stack, and what change makes the original approval stale.
On October 13, SBS announced an AI Foundation for generative and agentic AI in core banking, saying it can run in private cloud, managed cloud, or on-premises environments without data leaving the institution’s environment. It also says Scottish Building Society is using the platform on AWS. The SBS announcement is a useful deployment signal—not independent proof that a particular bank’s data, access, retention, or regulatory obligations are satisfied.
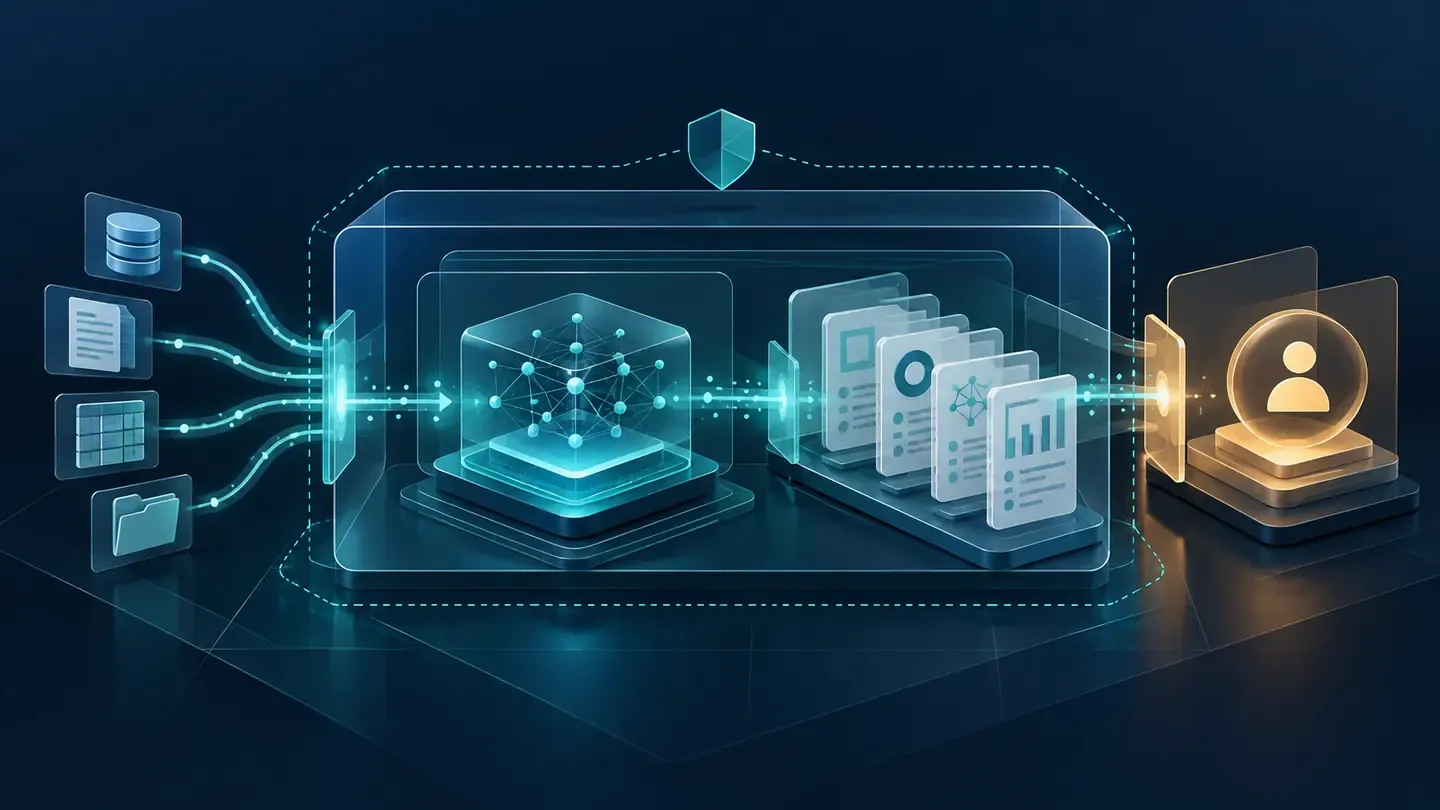
The operational question is narrower: can a reviewer reproduce the allowed deployment boundary for this workload from current evidence? This article provides a Sovereign AI Deployment Boundary Attestation for that task. It records a bounded claim and its evidence; it never certifies a system as sovereign, legal, compliant, secure, or appropriate for an investment decision.
This is deliberately different from a financial-data MCP control contract, which governs licensed source access for research, and an AI core-banking change evidence pack, which connects a business-rule change to tests. Here, the unit of control is one deployable AI runtime and its data/operations boundary before production acceptance.
Define the boundary before debating the label
“Data stays in our environment” is too vague to review. Treat it as several falsifiable claims:
| Claim to attest | Evidence a reviewer can inspect | Do not substitute |
|---|---|---|
| Approved data enters the workload | Data classification, approved sources, minimization decision | A generic privacy statement |
| Processing is in an approved location | Region, account/subscription, network diagram, routing policy | A vendor region map |
| No unapproved egress path exists | DNS/proxy allowlist, endpoint inventory, private-link or firewall evidence | “No one plans to export data” |
| Operators are within the approved boundary | Named roles, privileged-access path, support terms, break-glass record | An organization chart |
| Prompts, outputs, logs, and backups have bounded retention | Configuration export, retention policy, deletion evidence | A verbal promise of zero retention |
| A material change reopens review | Version/change record and explicit reapproval triggers | Last year’s architecture approval |
The vocabulary matters because different artifacts can carry sensitive information. Prompts can include customer details; embeddings can retain a recoverable relationship to source material; observability traces may store tool arguments; backups can outlive an intended deletion. A private inference endpoint does not settle any of those paths.
NIST describes the AI Risk Management Framework as voluntary guidance for incorporating trustworthiness considerations across design, development, use, and evaluation. Use its Govern, Map, Measure, and Manage framing to assign an owner, map the system and data flows, test the stated boundary, and route exceptions. Do not convert that framing into a compliance conclusion.
Build one deployment-boundary attestation
Create one record for a deployable workload, such as a contact-center summarization service or an internal operations copilot. Do not let a broad platform approval silently cover a new model, an external tool, a new vector store, or a new logging destination.
attestation_id: SAI-BOUNDARY-2026-1015-001
scope: "Production-acceptance evidence only; no compliance certification"
status: EVIDENCE_INCOMPLETE
workload:
  business_purpose: "Internal servicing-note drafting"
  accountable_owner: "banking-operations-owner"
  environment: "production"
  approved_region: "approved-region-reference"

data_boundary:
  allowed_classes: ["internal-operations", "approved-customer-data"]
  prohibited_classes: ["unapproved-secrets", "unmasked-production-export"]
  prompt_location: "approved-runtime-reference"
  inference_location: "approved-runtime-reference"
  output_location: "approved-application-reference"
  log_location: "approved-observability-reference"
  backup_location: "approved-backup-reference"
  retention_reference: "retention-policy-version"

egress_and_operations:
  approved_endpoints: ["named-inventory-reference"]
  blocked_or_unverified_paths: ["public-model-endpoint", "unreviewed-plugin"]
  network_evidence: "firewall-or-private-link-evidence-reference"
  operator_roles: ["platform-operator", "security-reviewer"]
  support_access: "approved-support-path-or-none"
  privileged_access_evidence: "access-review-reference"

verification:
  tested_on: "test-run-reference"
  negative_tests:
    - "route a synthetic sensitive field to an unapproved endpoint"
    - "attempt log export outside the approved environment"
    - "change model or tool configuration without a new approval"
  observed_result: "PASS_FAIL_OR_NOT_RUN"
  unresolved_gaps: ["none-or-named-gap"]

reapproval:
  triggers: ["region-change", "model-change", "new-tool", "logging-change", "support-access-change"]
  exception_owner: "authorized-risk-owner"
  exception_expiry: "date-or-not-approved"
  approval_reference: "immutable-change-or-ticket-reference"
Use references, not copied secrets, customer records, credentials, or raw network captures. An attestation should let an authorized reviewer locate evidence without turning the record itself into a new sensitive-data store.
Separate data paths from operator paths
Teams often draw only the application path: user → model → answer. A deployment decision needs two maps.
The data path includes ingestion, prompt assembly, retrieval, inference, output delivery, telemetry, deletion, and backup. The operator path includes customer administrators, cloud administrators, vendor support, incident responders, and any subprocessors that can administer a control plane. A claim about data residency may be true while a privileged support path, diagnostics export, or model-management service sits outside the intended operational boundary.
Microsoft’s AI workloads and sovereignty guidance distinguishes lifecycle phases such as ingestion, embedding, training, evaluation, deployment, inference, monitoring, and retirement. Its examples are cloud-platform guidance, not a banking rulebook, but the lifecycle view is a useful challenge: every phase named in the architecture needs an owner, location, and evidence reference.
For a bank or credit union, the answer can legitimately be “unknown.” Record that answer. An unknown log destination is not a low-risk claim; it is an incomplete attestation awaiting evidence or a scoped exception.
Use a claim–evidence–owner–expiry decision matrix
The matrix prevents an attractive label from becoming the approval artifact.
| Claim | Evidence reference | Accountable owner | Expiry / reapproval event | Review result |
|---|---|---|---|---|
| Prompts remain in approved processing scope | Runtime configuration export and network test | Platform owner | New endpoint, region, or model | COMPLETE / GAP |
| Diagnostics do not create unapproved copies | Logging configuration and retention test | Security owner | New telemetry tool or retention change | COMPLETE / GAP |
| Privileged support is bounded | Support terms and access review | Vendor manager | New support tier or emergency access | COMPLETE / GAP |
| Fallback behavior preserves the boundary | Failure-mode test and routing policy | Service owner | New fallback model or provider | COMPLETE / GAP |
Do not use an AI-generated summary as evidence. It can organize supplied facts, flag blank fields, and produce a reviewer checklist. The source configuration, signed change record, test output, or contract remains the evidence.
Copyable prompt: find missing proof, never approve the boundary
Use this only with authorized, non-sensitive references. It produces a gap list, not a risk rating or approval.
You are an evidence-pack assistant for a financial-services AI deployment.

Given the supplied attestation fields and evidence references:
1. List each claim about data location, egress, logging, backup, operator access, and fallback routing.
2. Mark a claim EVIDENCE_PRESENT only when a supplied reference directly supports it.
3. Mark a claim EVIDENCE_MISSING when the reference is absent, stale, ambiguous, or describes a different environment.
4. Identify whether a listed reapproval trigger applies to the proposed change.
5. Produce questions for the accountable owner. Do not infer a region, retention period, subprocessor, legal obligation, or security control.
6. Do not certify sovereignty, compliance, safety, or production readiness. Do not approve deployment.

Return: claim | supplied evidence reference | status | owner question | required human decision.
Test the attestation before production
Run negative tests in a controlled environment. The aim is not to prove that nothing can ever leave a boundary; it is to discover whether the asserted controls behave as described.
1. Unapproved endpoint test
Attempt to route synthetic sensitive data to a non-allowlisted endpoint. The expected result is a documented block, alert, or explicit failure—not a successful response with a later manual explanation.
2. Telemetry expansion test
Enable a new diagnostic setting in a nonproduction clone. Verify where prompt fragments, tool arguments, and error traces would be stored, who can read them, and whether the change triggers reapproval.
3. Fallback-route test
Simulate an unavailable model or regional service. Verify that any fallback model, endpoint, or queue is already in the attestation. A resilience mechanism that changes the processing boundary is a governance event.
4. Support-access test
Review a support escalation and break-glass path. Record the initiating role, approval, time limit, activity log, and evidence that access was removed. “Support may need access” is not an evidence record.
The AI banking integration cutover decision card can then consume a completed attestation as one input to a production decision. It should not compensate for missing boundary evidence.
Measure evidence quality, not a sovereignty score
Avoid a single “sovereignty score.” It masks a missing log path behind unrelated green controls. Track operationally useful measures instead:
- Percentage of production AI workloads with current attestations.
- Percentage of claim rows linked to directly inspectable evidence.
- Count and age of unresolved boundary gaps.
- Percentage of material changes that triggered reapproval before deployment.
- Negative-test pass rate, reported with failed-path details rather than as a generic safety score.
These measures reveal whether a bank can keep a deployment claim current; they do not establish legal compliance, data-residency eligibility, security, model quality, or customer fairness.
What this attestation cannot do
This artifact does not replace a bank’s legal analysis, privacy impact assessment, vendor due diligence, information-security program, model-risk management, contractual review, or authorized change process. It cannot prove that a vendor statement is complete, that a configuration has no undiscovered path, or that a deployment is permitted in a specific jurisdiction.
It also is not investment, legal, regulatory, security, or operational advice. Use qualified internal owners and advisers to evaluate the actual system, contracts, records, and applicable requirements before production use.
Sources
- SBS: “SBS Launches Banking’s First Sovereign AI Platform”
- NIST AI Risk Management Framework
- Microsoft Learn: AI workloads and sovereignty
About Enis
AI Engineer specializing in Machine Learning and LLMs. Combining Computer Engineering and Economics to build data-driven financial tools.